Key points
- Researchers documented hardware tampering techniques in a recent WiFi security study.
- Attackers used UART lockdowns to prevent detection of modifications to flash memory.
- The findings were shared on r/netsec by user gid0rah.
A recent security study reveals how attackers compromise WiFi devices by physically altering hardware components. Researchers demonstrated that tampering with flash memory chips allows malicious changes to persist on the device. This method bypasses standard software security checks that rely on unmodified hardware states.
In plain English
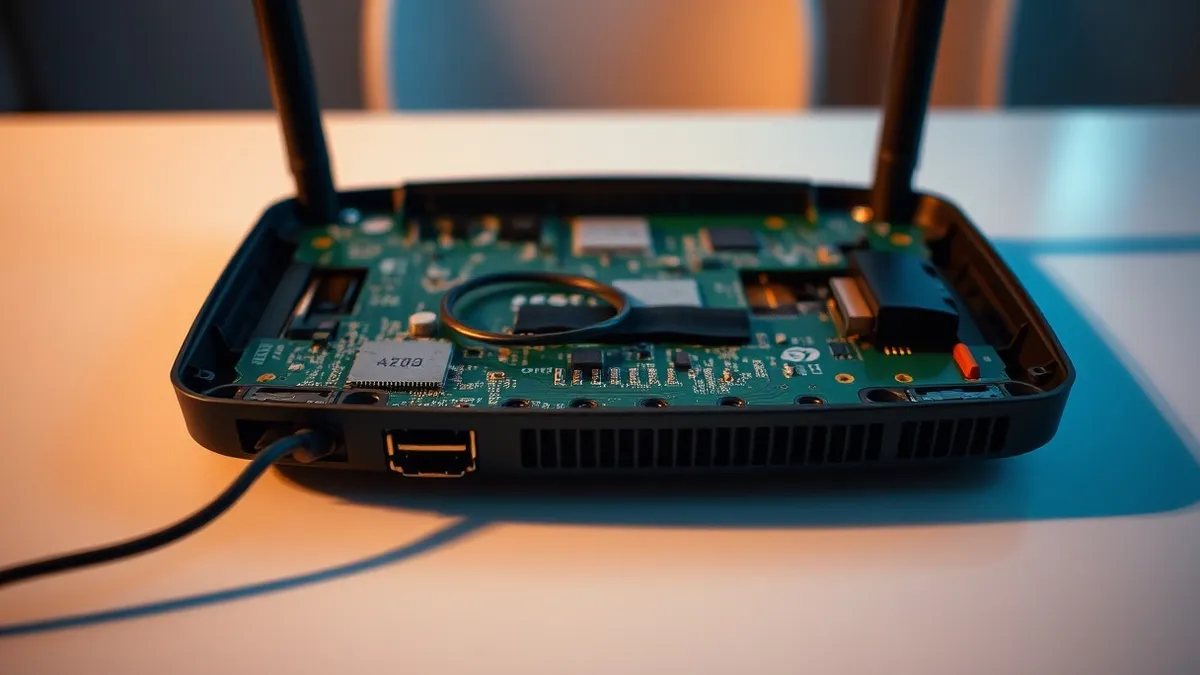
WiFi devices store their operating instructions in small memory chips called flash memory. Attackers can remove these chips, change the data inside them, and put them back. This process is known as hardware tampering. By altering the physical chip, attackers can install backdoors or steal data without triggering software alarms that monitor for changes in the code.
The background
The study highlights the use of UART lockdowns as a key part of the attack chain. UART ports allow engineers to access the device for debugging and maintenance. Attackers disable or lock these ports to prevent security researchers from inspecting the device. This lockdown hides the evidence of the tampered flash memory and stops anyone from resetting the device to a safe state.
What changes now
The report was submitted to the r/netsec community by user gid0rah. It serves as a warning about the physical security risks of network hardware. Organizations that manage sensitive data must consider that software updates alone may not protect against hardware-level compromises. Physical access to devices remains a significant vulnerability for WiFi infrastructure.
What to do and how to stay safe: WiFi security
- Physically inspect network hardware for signs of tampering, such as loose screws or altered chips, during routine maintenance checks.
- Restrict physical access to server rooms and network closets to authorized personnel only to prevent unauthorized hardware modifications.
- Monitor device logs for unexpected resets or failures that might indicate an attempt to bypass security through hardware manipulation.
- Verify the integrity of device firmware using cryptographic signatures before deploying new hardware into your network environment.
Step-by-step guide: Smartphone Security Updates for Small Business Operations
General security guidance from the Patch Review newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
What is UART lockdown in this context?
UART lockdown is a technique where attackers disable serial access ports to prevent security researchers from inspecting or resetting the compromised device.
How do attackers alter the flash memory?
Attackers physically remove the flash memory chip from the device, modify its contents, and reattach it to hide malicious changes from software security checks.
Where was this information published?
The findings were shared on the r/netsec subreddit by user gid0rah, detailing the hardware tampering and UART lockdown methods used in the study.